Fix Your AI Risks
...and unlock innovation
Building and adopting AI solutions is often easier than securing and governing them.
Generic AI security controls rarely match operational reality.
SafeDescent secures and supervises AI using risk controls and evaluations tuned to your AI use cases.
A deliberately simplified view. In engagements we work with a methodology that incorporates the OWASP standards for LLM and agentic security, NIST AI RMF, and MITRE ATLAS; on the regulatory side, ISO/IEC 27001, ISO/IEC 42001, and the EU AI Act. We continuously track new risks, research, and security controls.
From the first call to a safer system.
Risk Audit and Engagement
We build prioritized action plan against your risk profile.
Measurable security
A safer system. You own the IP.
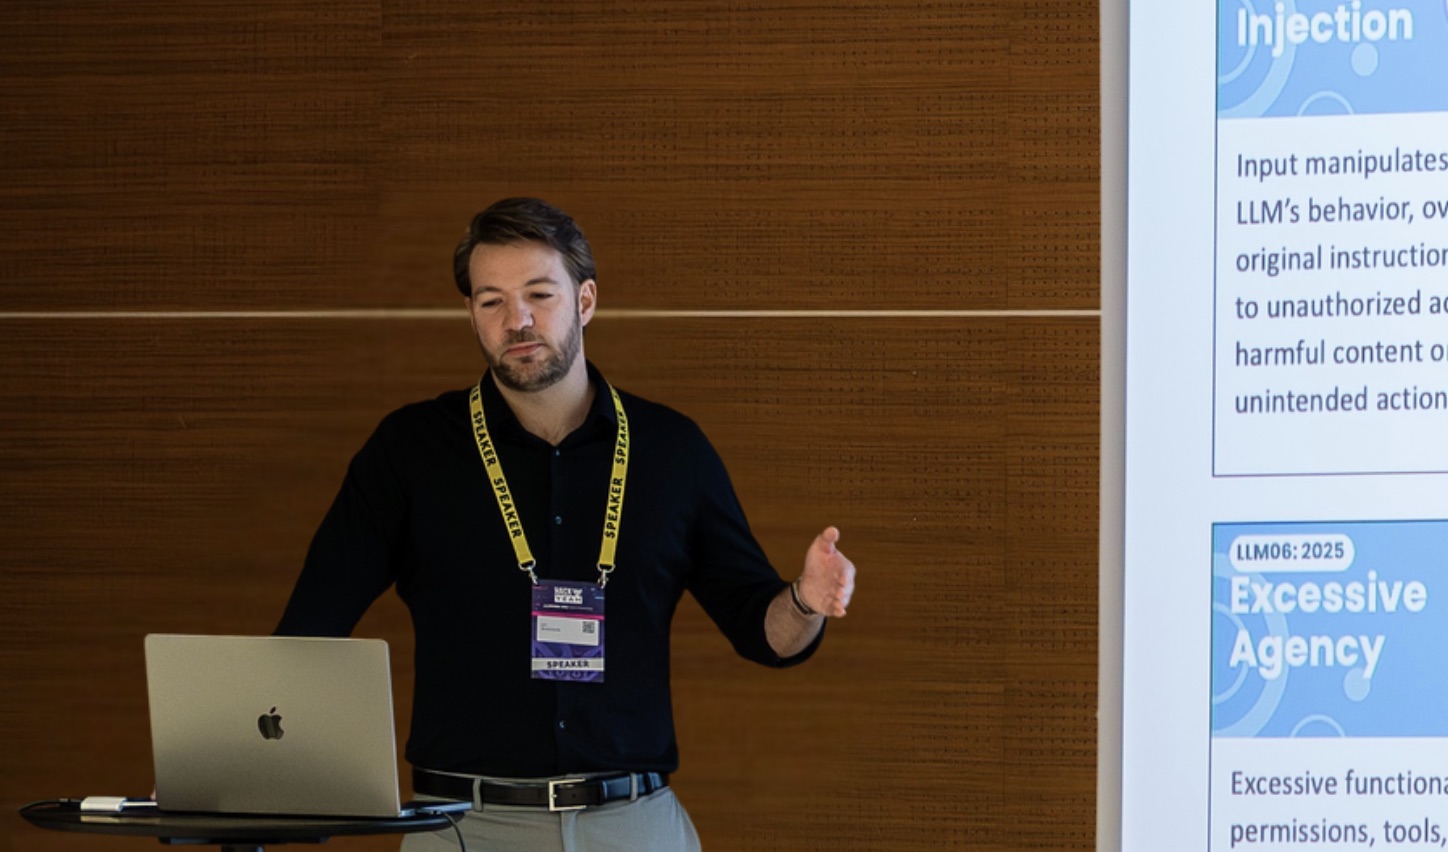
The person behind the methodology and delivery.
Hi, I’m Jan Broniowski and I run SafeDescent.
- AI architect for 10+ years, in LLM security from the very early days (GPT2)
- Contributor to initial OWASP Top 10 for LLMs, author of security blueprints
- Experience as senior managing AI consultant, advising 50+ Fortune 500 AI projects
- Led LLM pentest teams; ran AI security research teams
- Speaker at conferences, podcasts and UK universities seminars
My LinkedIn.
Measure your AI risk before we ever talk.
A basic AI risk self-check, free. Plain questions about how your AI system is built and used; you leave with a risk classification and the specific risks to look at.
Get the self-check- Written from experienceDistilled from real reviews of real AI systems: the questions we ask in engagements and the failure modes we keep finding.
- Basic on purposeIt covers the surface. The things a questionnaire cannot catch are what an engagement is for, and we say so at the end.
- Optimized for usefulnessYou leave with a risk classification and specific risks to check, not a score for a slide.